C:\ZYAGA\WORK\NMAPYOURSELF> TYPE README.TXT
NmapYourself
Scan yourself over the internet with Nmap and see what hackers see when they scan your ports. Free, for almost twenty years.
ERROR 404: HOST OFFLINE. THIS PROJECT IS ARCHIVED, SO THERE IS NO LIVE LINK.
NmapYourself was a free web front end to the Nmap security scanner that only ever scanned one address: yours. Pick a scan type, the ports and the options, agree that you have full rights to the network you're about to scan, and it runs Nmap against your connection from across the internet and shows you the exact command and its output.
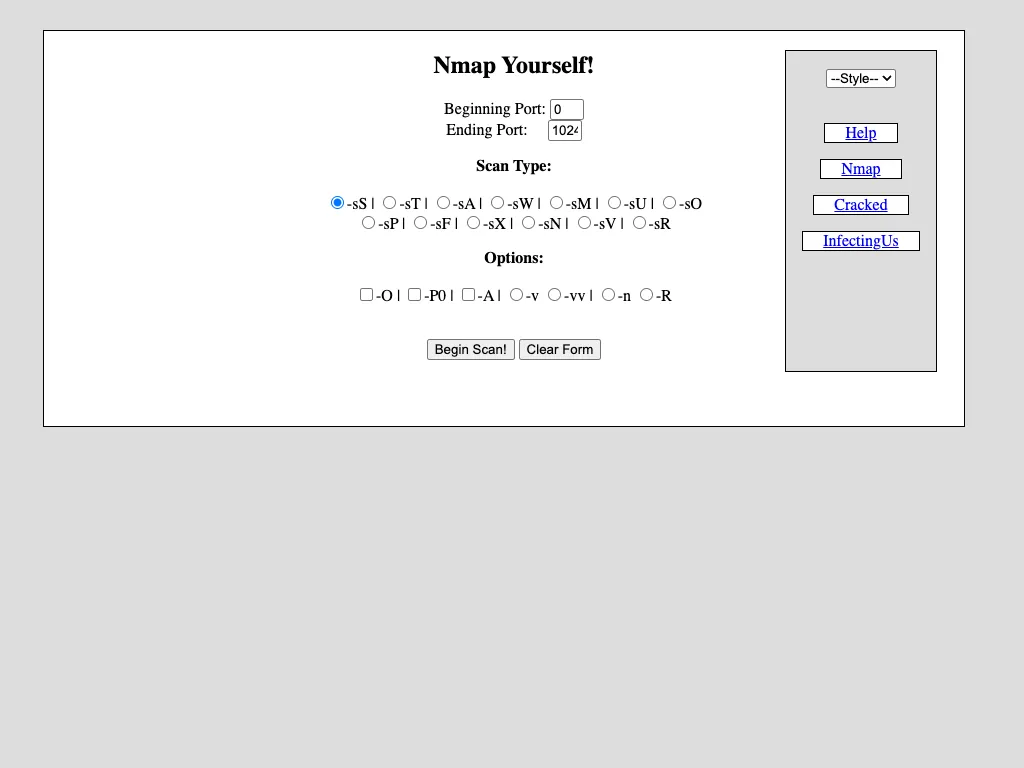
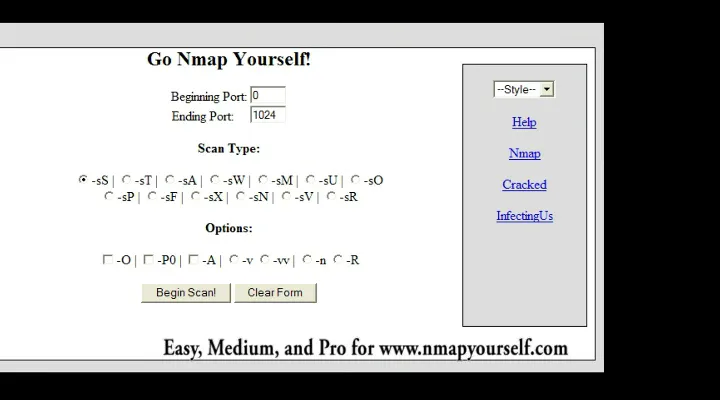
It started in 2007 alongside Cracked Productions, with every Nmap scan type as a radio button and Easy, Medium and Pro styles, and was rebuilt on Bootstrap later. Behind the form, a small setuid C wrapper ran Nmap, one scan per address every three minutes. It kept running until 2026.
- TYPE
- Online port scanner
- PLATFORM
- Web
- YEARS
- 2007 – 2026
- ROLE
- Built and ran it: the PHP front end, the wrapper around Nmap and the server.
- STACK
- PHP / Nmap / C (setuid wrapper) / MySQL / Bootstrap / jQuery
- 3,000+scans logged since 2014
- 19years online, 2007 to 2026
- 13Nmap scan types in the 2007 version
C:\ZYAGA> DIR /FEATURES 機能
[01]
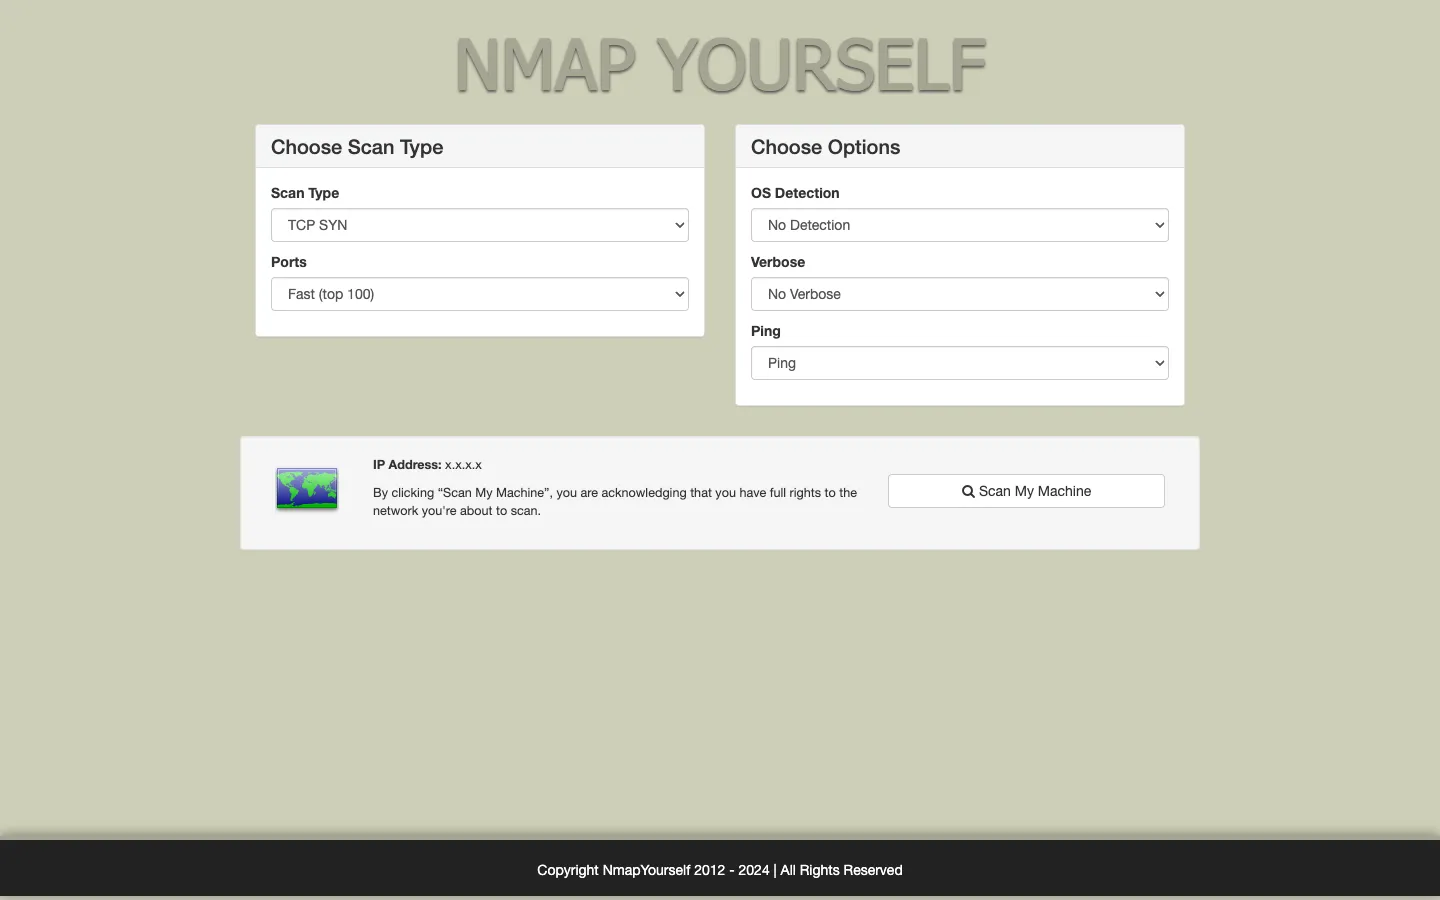
Choose your scan
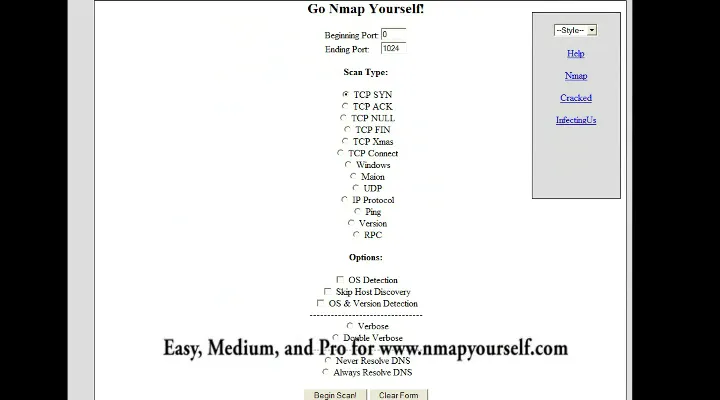
TCP SYN, Connect, UDP, service version, FIN, Xmas and NULL scans; the top 100, top 1,000 or all ports; OS detection, verbosity and ping options.
[02]
Scanning from across the web
The results page loads while Nmap runs against your address from the server.
[03]
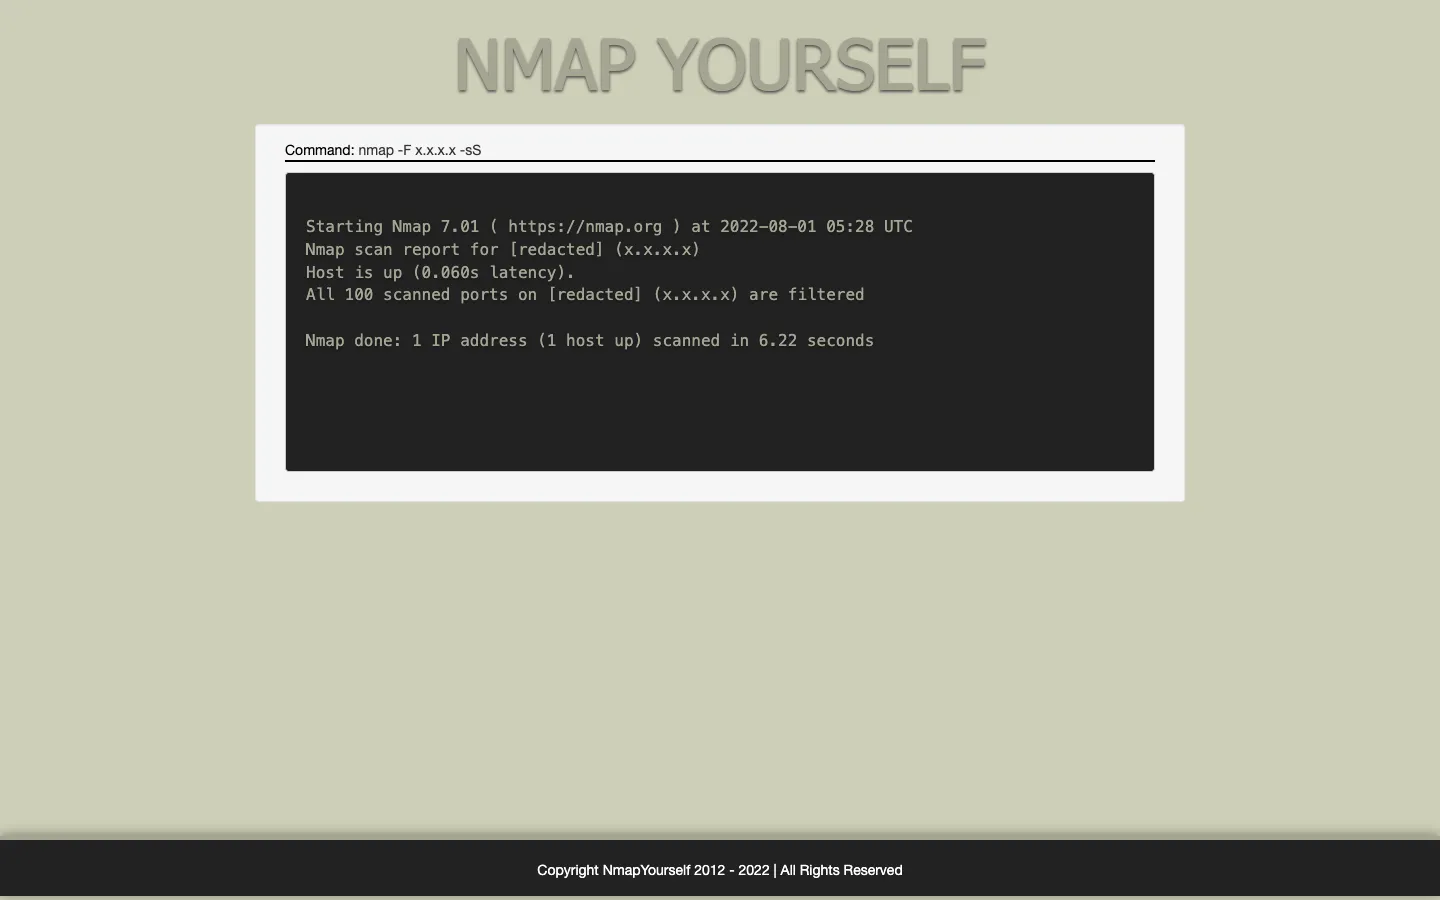
See what hackers see
The exact Nmap command, then its output: every open port on your connection.
C:\ZYAGA> LOG --HISTORY 歴史
2014 – 2026
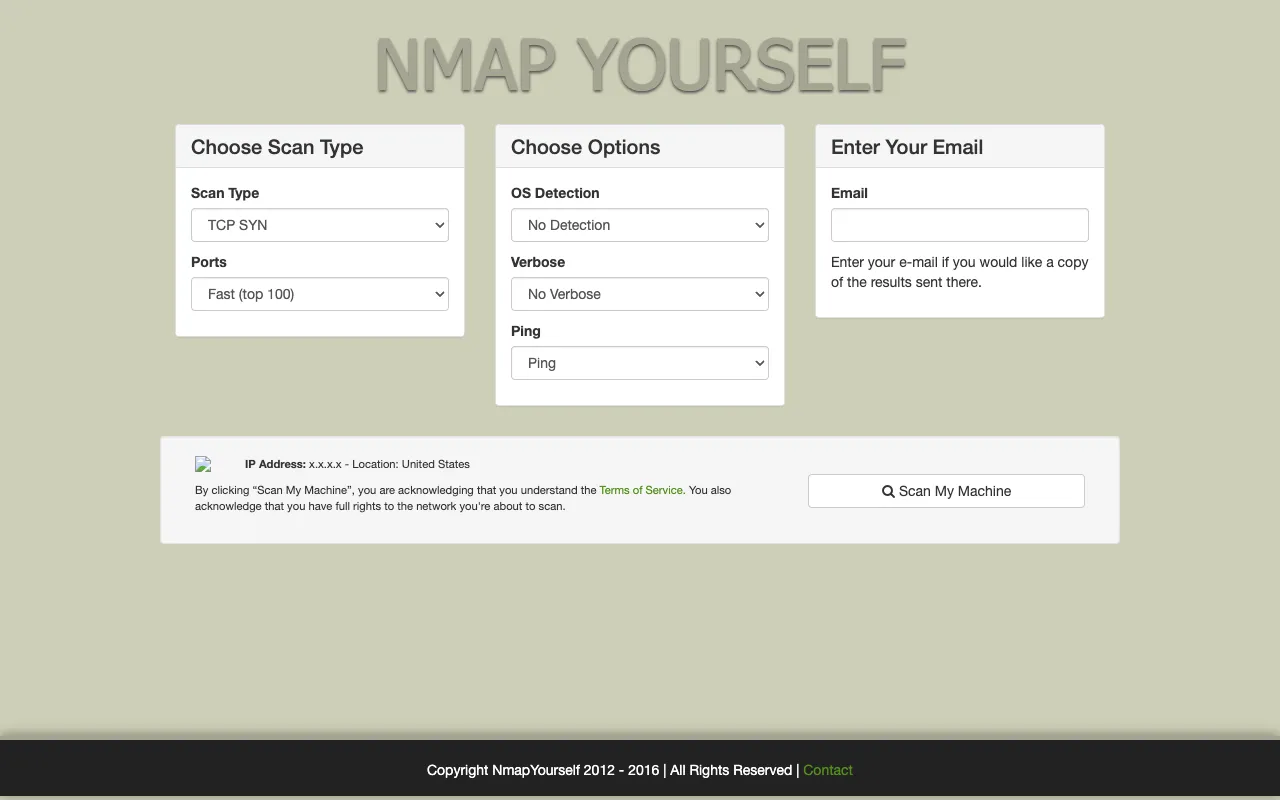
Bootstrap rebuild
Plain-language scan options, asynchronous results, and until 2016 an option to email them to yourself.
2007 – 2008
Go Nmap Yourself!
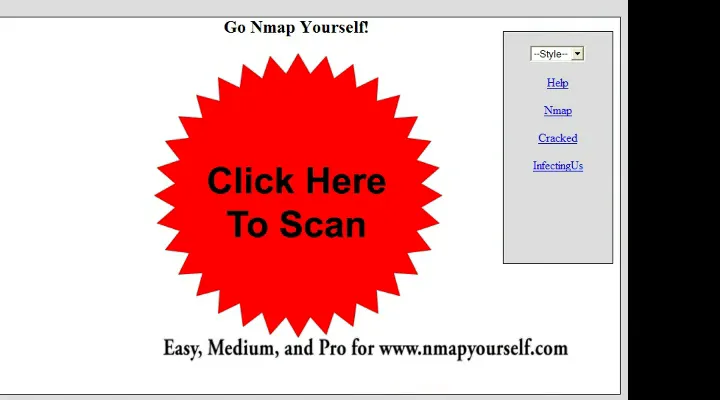
The original: a big Click Here To Scan button, then Easy, Medium and Pro pages with every Nmap flag.

< NEWER: zyaga.com, before this oneOLDER: RainbowCrack Online >